Digital Security
Layered Protection for Every Part of Your Digital Operations
Protect identities, systems, applications, and information with coordinated controls, engineer-validated analysis, and practical plans for response and recovery.
Investigate with Context
AI-assisted analysis highlights activity worth reviewing; experienced engineers validate findings and guide the response.
Prepare to Recover
Incident planning and recovery testing help your teams respond when preventive controls are not enough.
Security Works Best When Controls Work Together
Protecting a business takes more than one tool. A stolen password can put information at risk even when a network is well defended; a compromised device can expose applications despite careful access settings. Intelligence Inc. approaches digital security as an ongoing responsibility across identities, systems, applications, and information. Based in Allen, Texas, we serve organizations with varied operational needs by examining how people use technology, where sensitive data moves, and which services are essential to daily work. We then help align access management, endpoint, network, email, and cloud controls with those realities. AI-assisted analysis can organize security signals and surface activity for investigation, while experienced engineers assess the evidence and recommend practical action. Employee guidance, clear incident responsibilities, regular reviews, and tested recovery plans extend protection beyond prevention, helping the organization adapt as its technology and risks change.
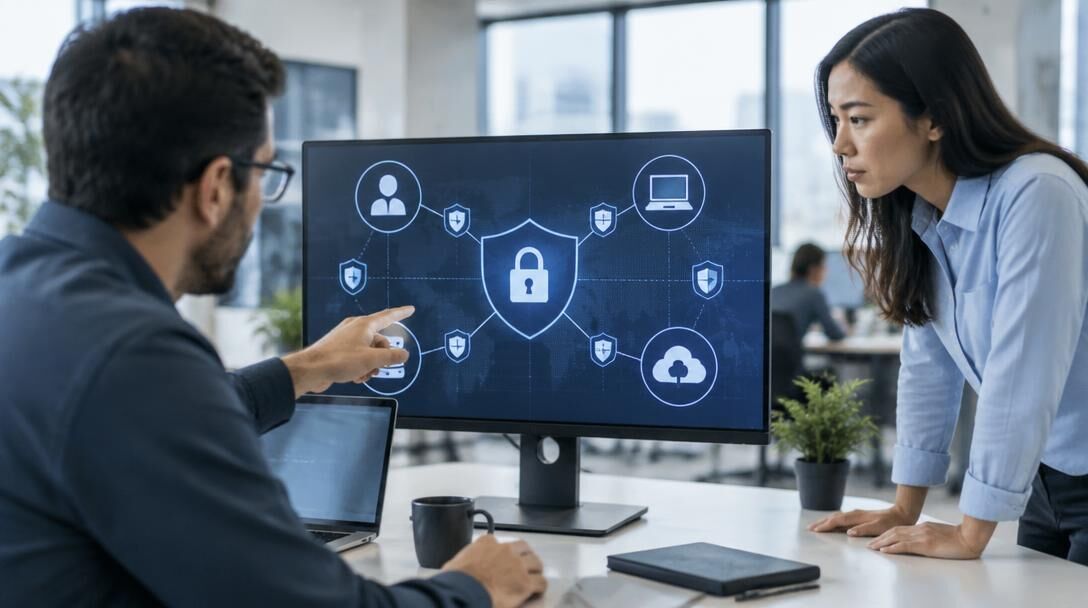
Connected Defenses Across Your Environment
Identity Verification
Role-Based Access
Privileged Account Oversight
Device Health Monitoring
Endpoint Threat Protection
Network Traffic Visibility
Network Segmentation
Email Threat Filtering
Phishing Awareness
Cloud Access Governance
Cloud Configuration Review
Application Permission Checks
Security Event Investigation
Employee Security Guidance
Recovery Readiness Reviews
From Signals to Informed Action
Step 1
First, AI-assisted analysis organizes events across identities, endpoints, email, networks, and cloud services so relevant activity is easier to review.
Step 2
Next, it highlights unusual patterns and potential exposures for investigation without treating every alert as a confirmed threat.
Step 3
Finally, experienced engineers validate findings against your environment and recommend a response suited to the risk.
Step 1
Identify the Activity
Gather alerts, reports, and system events to establish what happened and which accounts, devices, or services may be involved.
Step 2
Assess the Impact
Examine the evidence, affected information, and business context to distinguish an actual incident from routine or misleading activity.
Step 3
Define the Response
Prioritize containment and corrective actions, considering application dependencies, access needs, and the effect of changes on operations.
Step 4
Coordinate and Verify
Work with responsible teams to carry out technical measures, confirm their results, and document findings for follow-up review.
Plan for What Prevention Cannot Stop
Layered controls reduce exposure, but an incident can still interrupt access to essential systems or information. Recovery planning starts by identifying critical work, the applications and data it relies on, and how long the organization can operate without them. Those needs guide backup arrangements, restoration priorities, and the people responsible for decisions when normal operations are disrupted.
Make Recovery Arrangements Practical
Backups are most useful when they cover the right information and can be restored within a timeframe the business can accept. Our engineers review where data is held, how systems depend on one another, and what access may be needed during restoration. Testing helps uncover missing steps and assumptions before an incident, while regular reviews keep the plan aligned with changes to applications, infrastructure, and business priorities.
Everyday Habits That Strengthen Security
- Use unique passwords and an approved password manager.
- Approve multifactor prompts only when you initiated the sign-in.
- Lock your screen when stepping away from your workspace.
- Install approved updates when your IT team requests them.
- Use only authorized accounts for sensitive business tasks.
- Review sharing permissions before sending confidential files.
- Check unexpected emails for unusual requests or altered sender addresses.
- Verify payment or access changes through a trusted channel.
- Avoid opening unfamiliar attachments or shortened links.
- Watch for sign-ins, alerts, or device behavior you cannot explain.
- Keep business information out of unapproved AI tools.
- Check AI-generated answers before relying on them for decisions.
- Report suspicious messages using your organization’s approved process.
- Tell IT promptly if you clicked a questionable link.
- Flag unexpected account permissions or shared-file access.
- Describe what happened, when it happened, and which systems were involved.
- Preserve relevant messages or alerts; do not investigate on your own.
- Follow response guidance before reconnecting an affected device.
Six Signals That Guide Security Priorities
100
Access reviews: identify permissions that no longer match current roles.
100
Endpoint coverage: reveal devices missing updates or protective controls.
100
Email trends: show which suspicious messages warrant closer attention.
100
Cloud changes: surface new configurations and shifting usage patterns.
100
Incident findings: turn investigated events into targeted improvements.
100
Recovery tests: expose gaps before essential systems need restoration.
Discuss Your Protection and Resilience Priorities
Contact Intelligence Inc. to review your security concerns, changing requirements, and recovery needs. We can help identify practical next steps for protecting the people, systems, and information your organization relies on.